Language Settings
Select Website Language

GDPR Compliance

We use cookies to ensure you get the best experience on our website. By continuing to use our site, you accept our use of cookies, Privacy Policy, and Terms of Service.

Filters

Channels
Topics
Other Filters

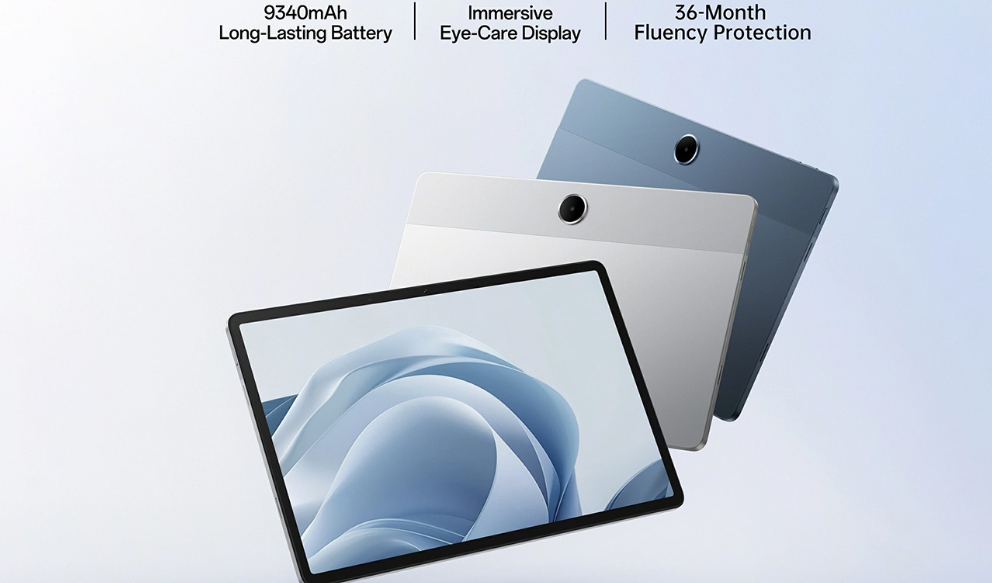
OPPO Teases New Tablet for India Expected Features and Launch

OPPO teases a new tablet for India, but its launch date, price and final specifications remain unconfirmed. By News National Editorial Team OPPO has teased the arrival of a new tablet for the Indian market, raising expectations of an expansion in its large-screen device portfolio. Technology coverage published in October has linked the teaser to the OPPO Pad 5 Pro, although the company has not yet confirmed the Indian launch date or retail price in the reporting available for this article. The announcement comes as tablet makers compete to attract consumers seeking larger displays, improved performance and accessories that support work and study. What Is Known About the India Teaser? Reports describe OPPO's teaser as an indication that a new tablet is being prepared for the Indian market. However, a teaser does not establish the final product name, complete Indian specifications or confirmed sale date. Some reports have suggested that the anticipated device could share hardware with the OnePlus Pad 4. That possibility should be treated as an expectation rather than a confirmed specification until OPPO releases official details. What Buyers Should Watch For The most important details to confirm at launch will include the display size and refresh rate, processor, RAM and storage options, battery capacity, charging speed, software support and accessory compatibility. Indian buyers should also look for official information about warranty coverage, service availability, pricing and whether a keyboard or stylus is included or sold separately. Competition in India's Tablet Market The Indian tablet market serves a wide range of customers, from students and families to professionals who need a portable work device. Premium tablets compete on processing power, display quality and productivity features, while more affordable models focus on everyday applications and online learning. OPPO's next announcement could provide another option for buyers, but a purchase decision should wait until the company confirms the device's specifications and price for India. News National verification note: The India teaser is reported by technology media. The Indian launch date, final product name, pricing and complete specifications remain unconfirmed in the cited report. News National should update this story when OPPO publishes an official announcement. Source: My Mobile Indiahttps://www.mymobileindia.com/oppo-teases-new-tablet-and-enco-x4-for-india-pad-5-pro-and-flagship-earbuds-coming-soon/

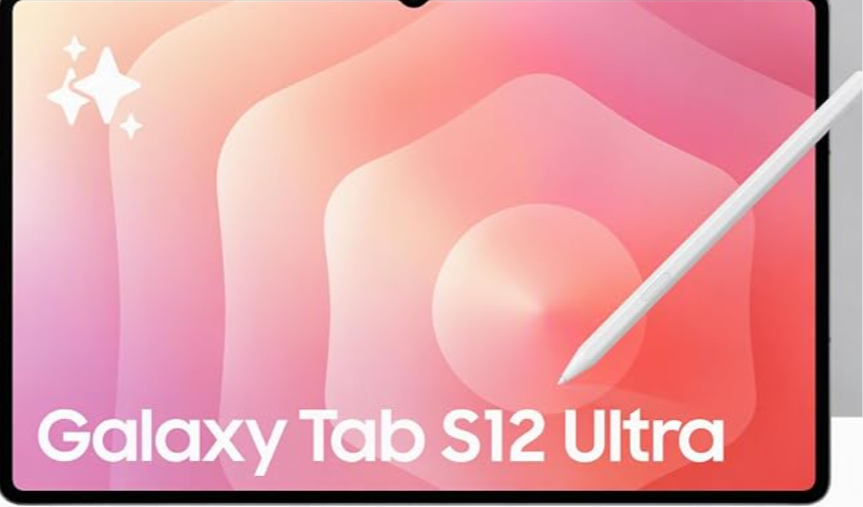
Samsung Galaxy Tab S12 Ultra, S12+ India Price and Specs

Samsung Galaxy Tab S12 Ultra and S12+ arrive in India with AMOLED displays, Dimensity 9500, S Pen and batteries up to 11,600mAh. By News National Editorial Team Samsung's Galaxy Tab S12 Ultra and Galaxy Tab S12+ have entered the Indian market, bringing premium AMOLED displays, the MediaTek Dimensity 9500 processor and Galaxy AI features to the company's flagship tablet range. Samsung announced Indian availability beginning October 7, 2026. The new models target users who want large screens for work, studying, digital art, video editing and entertainment. India Pricing and Configurations Samsung's announced starting prices are ₹1,49,999 for the Galaxy Tab S12 Ultra and ₹1,29,999 for the Galaxy Tab S12+. The company lists Wi-Fi and 5G versions with 256GB and 512GB storage configurations. The Ultra model also has a 16GB RAM and 1TB storage configuration listed in Samsung's specifications. Prices vary by model, connectivity and storage. Buyers should check Samsung's official store for the exact configuration price and any applicable offers. Display and Performance The Galaxy Tab S12 Ultra features a 14.6-inch Dynamic AMOLED 2X display, while the S12+ has a 12.6-inch display. Both support a 120Hz refresh rate and peak brightness of up to 1,600 nits, according to Samsung. Both tablets use the MediaTek Dimensity 9500 processor. Samsung says the hardware is designed to support demanding applications, multitasking and AI-assisted workflows. Battery, S Pen and Durability The Ultra model has an 11,600mAh battery, while the S12+ includes a 10,600mAh battery. Both support 45W charging and include an S Pen. Samsung lists IP68-rated water and dust resistance for the series. Connectivity differs between the models: the Ultra supports Wi-Fi 7, while the S12+ supports Wi-Fi 6E. Both have 5G variants and Bluetooth 6.0. Should Buyers Consider the New Tablets? The large displays and stylus support make the tablets relevant to professionals, students and creative users. The premium pricing, however, means buyers should compare the cost with laptops and less expensive tablets before making a decision. For consumers who mainly stream video, browse websites or attend online classes, a lower-cost tablet may offer better value. Users who need advanced multitasking, drawing or demanding creative applications may benefit more from the flagship hardware. News National verification note: Prices, specifications and availability are based on Samsung's official India announcement. Offers and stock can change by retailer and configuration. Source: Samsung Newsroom Indiahttps://news.samsung.com/in/samsung-galaxy-tab-s12-series-prices-announced-for-indian-market-with-special-deals

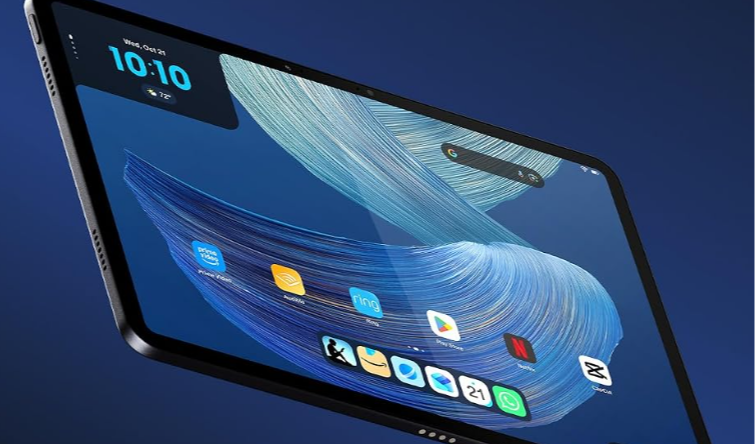
Amazon Alexa Tablets Launch With Android and Alexa+ AI

Amazon unveils new Android tablets with Alexa+ AI and Google Play Store access, including the 12-inch Alexa Tablet 12 Pro. By News National Editorial Team Amazon has announced a new range of Android-powered tablets featuring its Alexa+ artificial intelligence assistant, marking a significant change in the company's tablet strategy. The new lineup includes the Alexa Tablet 12 Pro, Alexa Tablet 11 and Alexa Tablet 8, according to reports published on October 8, 2026. The move gives Amazon a more direct opportunity to compete in the Android tablet market, where consumers can choose from devices made by Samsung, Lenovo and other manufacturers. Google Play Store and Alexa+ Integration One of the most important changes is the adoption of Google's Android operating system with access to the Google Play Store. This could address a long-standing limitation of Amazon's Fire tablets, which traditionally relied on Amazon's own app ecosystem. Amazon is also emphasizing Alexa+, its AI-powered assistant, as a central feature of the new devices. The company is positioning the tablets for entertainment, everyday assistance and connected-home tasks. Alexa Tablet 12 Pro Features The premium Alexa Tablet 12 Pro features a 12-inch display with a 120Hz refresh rate and a 3:2 aspect ratio. Amazon has announced standard and anti-glare Nanomatte display options. The tablet also supports optional accessories, including a Pro Pen and Pro Keyboard, aimed at users who want to take notes, type documents or use the device for productivity. According to the launch coverage, the Alexa Tablet 12 Pro starts at US$499.99, while the Nanomatte version starts at US$549.99. Amazon has also announced smaller 11-inch and 8-inch models. What It Means for Tablet Buyers The launch highlights growing competition between traditional tablet manufacturers and companies building devices around AI assistants. Access to a broader Android app ecosystem may make the new products more flexible than earlier Fire tablets. However, buyers should check app compatibility, software-update commitments, regional availability and subscription requirements before purchasing. Alexa+ features and services may have separate eligibility or subscription conditions. News National verification note: The product lineup, Google Play Store access, display details and US pricing are based on launch reporting. Indian pricing and availability should not be assumed unless Amazon confirms them. Sources: Reuters: https://www.reuters.com/business/retail-consumer/amazon-launches-first-android-tablets-raising-prices-incorporating-alexa-2026-10-08/ TechCrunch: https://techcrunch.com/2026/10/08/amazon-unveils-new-alexa-tablets-with-alexa-and-google-play-store-access/

Gujarat Daman-Ganga Barrage ₹159.50-Crore Vapi Project

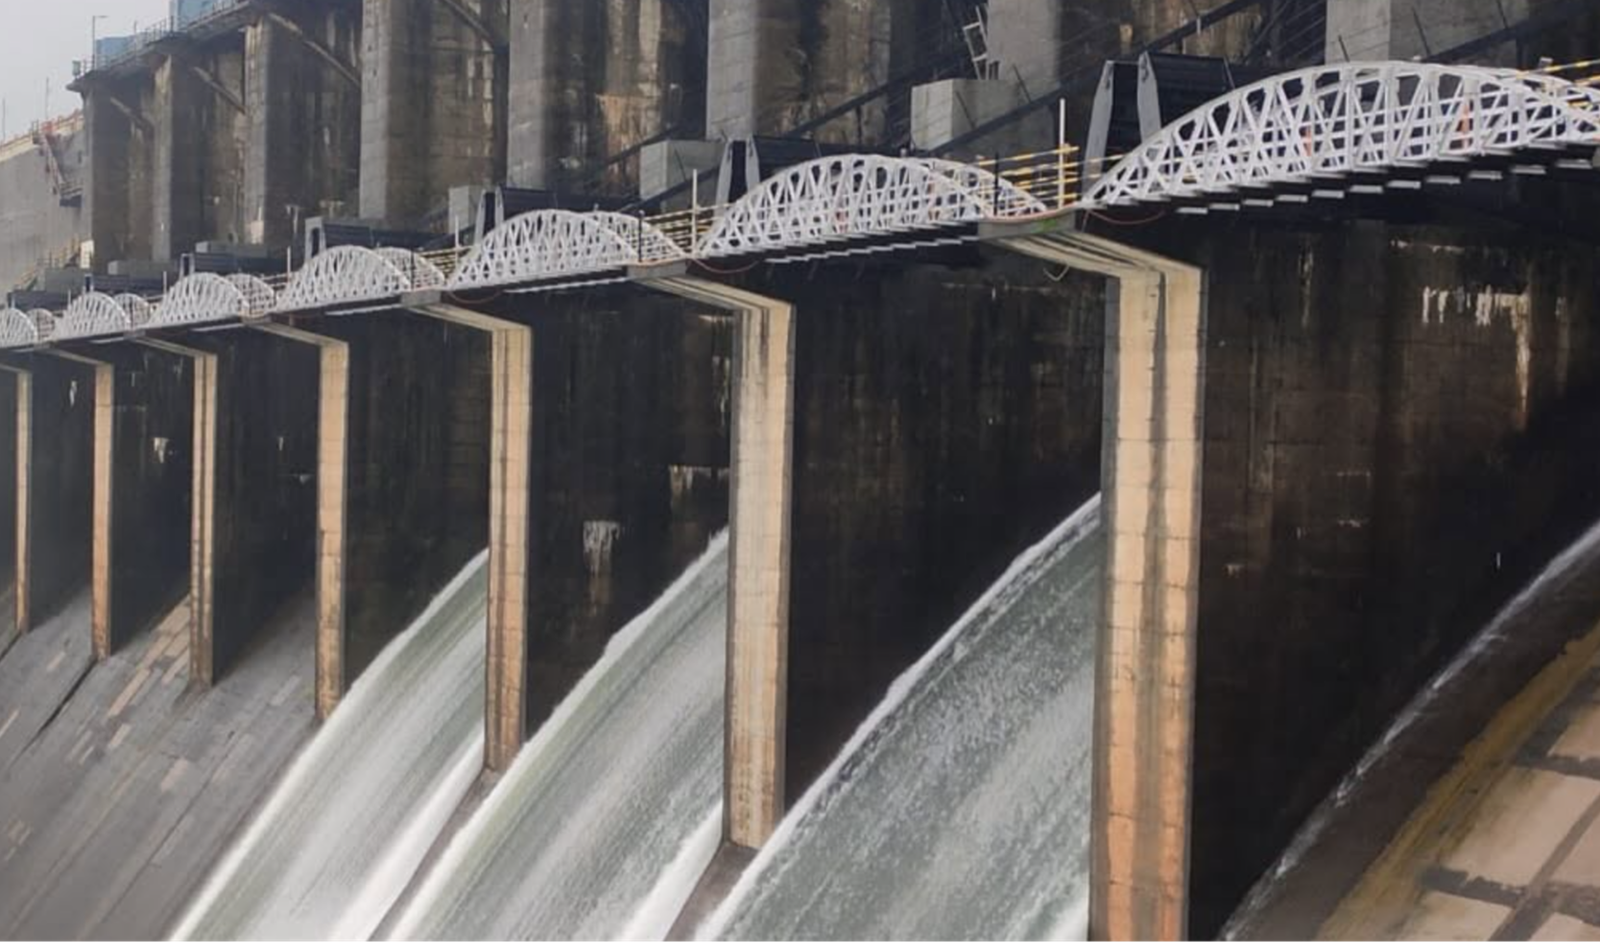
Gujarat’s ₹159.50-crore Daman-Ganga barrage near Vapi aims to improve irrigation, groundwater recharge and water security. By News National Editorial Team Vapi, Gujarat | October 12, 2026 Gujarat is preparing to move ahead with a ₹159.50-crore barrage project on the Daman-Ganga River near Vapi in Valsad district. The proposed infrastructure is intended to improve irrigation, increase water storage and support groundwater recharge, while strengthening water availability for households and industries in the surrounding region. According to reports published on October 12, an Engineering, Procurement and Construction (EPC) contract has been awarded for the project near Namdha village in Vapi taluka. The proposed barrage site is approximately three kilometres downstream of the existing Vapi Weir. The project is expected to create a gross storage capacity of 5.49 million cubic metres (MCM), providing an additional water-storage facility in an area with agricultural, industrial and municipal water requirements. Irrigation benefits for six villages One of the principal objectives is to improve irrigation access for farmers. The project is expected to create irrigation potential across approximately 549 hectares of agricultural land, with stored water supplied through a lift-irrigation system. The six villages identified as beneficiaries are Namdha, Chandor, Mohan, Eklahare, Nahuli and Jamburi. Improved access to irrigation could help farmers reduce their dependence on rainfall and make agricultural planning more predictable. Depending on water availability, crop requirements and local farming conditions, reliable irrigation may also create opportunities for additional cultivation. However, the projected irrigation benefits will depend on the completion of the infrastructure and the effective delivery and management of water. The announced potential should not be interpreted as evidence that all identified farmland is already receiving additional water. Water security for Vapi and nearby industries The barrage is also intended to support municipal and industrial requirements around Vapi, an important industrial centre in southern Gujarat. Figures cited in the project announcement show that during 2024–25, the existing Vapi Weir supplied 19 MCM of water for industrial use to Gujarat Industrial Development Corporation facilities, 7.30 MCM for water supply and 6 MCM to Vapi Municipal Corporation. The reported revenue from these supplies totalled ₹69.15 crore. The proposed barrage could add to the region's storage capacity and support future water requirements. Its actual contribution will depend on river flows, operating arrangements, demand and the amount of water available for allocation. The project announcement also identifies groundwater recharge as a potential benefit. Water stored upstream of the barrage could help replenish nearby groundwater sources, including existing tube wells in Vapi. The extent of any improvement in groundwater levels or quality will need to be assessed after the project becomes operational. Salinity control and wider development Another stated objective is to limit the movement of tidal water and reduce salinity intrusion into the riverbed. If effective, this could help protect freshwater resources in surrounding areas. The announcement also points to possible wider benefits, including better drinking-water availability, riverfront development, recreational facilities and improved connectivity. These should be treated as anticipated benefits rather than completed developments. For residents and businesses, the project's importance will ultimately depend on whether the additional storage translates into reliable and fairly managed water supplies. Construction progress, environmental safeguards, water allocations and the maintenance of the barrage will be important factors to monitor. As of October 12, 2026, the reported development concerns the planned project and its expected benefits. A confirmed construction-completion date and independently measured outcomes were not established in the reports reviewed. Sources DeshGujarat — ₹159.50-crore barrage to come up on Daman-Ganga River near Vapi, October 12, 2026 Asianet Newsable — Daman-Ganga barrage project near Vapi, October 12, 2026 Press Information Bureau — Revival of Daman Ganga River, March 27, 2026 — background on river-quality measures; not confirmation of this barrage's construction status.

Telangana FMGs Protest Over Internship Stipend Disparity

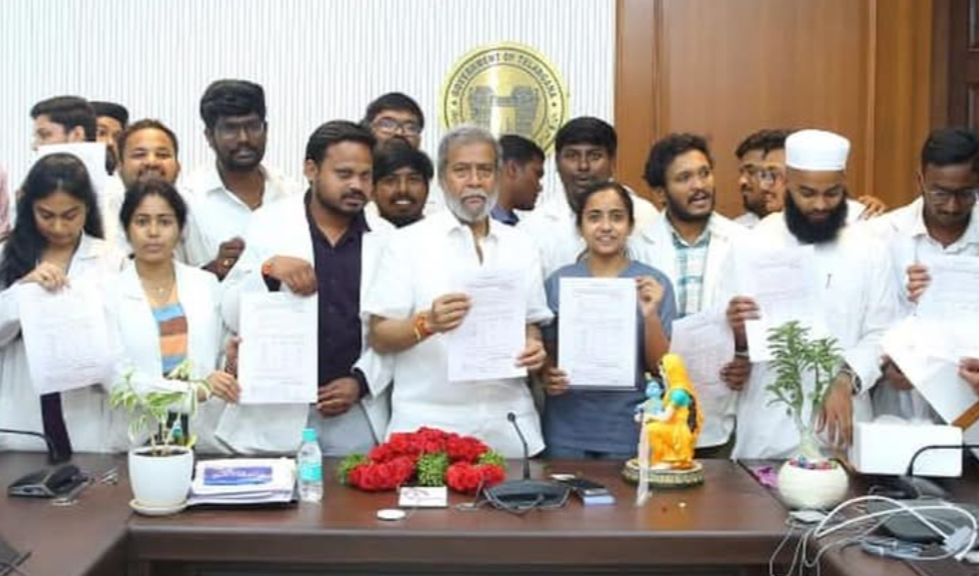
Foreign Medical Graduates in Telangana reportedly protest stipend differences as questions emerge over internship payments and hospital services By News National Editorial Team HYDERABAD, October 12, 2026: Foreign Medical Graduates (FMGs) in Telangana have reportedly withdrawn from internship duties to protest differences in stipends paid to them and graduates of Indian medical colleges. According to a report published by The Times of India on October 12, the interns are seeking parity in stipend payments. The dispute has drawn attention to the financial conditions faced by Indian students who complete medical education abroad and subsequently undergo compulsory internship training in India. Why the stipend dispute matters Foreign Medical Graduates must meet the applicable regulatory requirements before completing their medical training in India. Depending on their qualifications and eligibility, this process can include examinations, screening requirements and supervised internship training. Internship stipends help trainees meet living and transport expenses while they work in clinical settings. Differences in payments between institutions or categories of interns can therefore become a significant concern. The current dispute raises questions about the rules governing stipend payments, the responsibilities of individual medical colleges and the role of state authorities in addressing complaints. Possible impact on hospital services Any withdrawal from internship duties could affect the workload of other healthcare personnel. However, the extent of any disruption in Telangana hospitals has not been independently established in the information available for this report. Patients should check with their hospitals for information about appointment availability and any changes to services. Emergency medical care should not be delayed because of uncertainty surrounding the dispute. The next important developments will be an official response from the Telangana government, medical institutions and the relevant regulatory authorities. Clarification is also needed on the number of interns involved, the hospitals affected and whether discussions have begun to resolve the issue. Source: The Times of India — Hyderabad news

Hyderabad Police Restrict Midnight Celebrations Near Hussain Sagar

Hyderabad police reportedly restrict midnight birthday celebrations near Hussain Sagar after a fatal road accident involving a child. By News National Editorial Team HYDERABAD, October 12, 2026: Police in Hyderabad have reportedly introduced restrictions on midnight birthday celebrations and roadside cake-cutting events around Hussain Sagar following a fatal road accident involving a child, according to a report published by The Indian Express. The reported move has brought attention to road safety around popular gathering places, particularly at night when groups may assemble close to moving traffic. Road safety concerns Hussain Sagar and its surrounding areas attract residents and visitors for evening outings, celebrations and recreation. However, roadside gatherings can create risks when people stand on or near busy roads, especially in locations with limited pedestrian protection. The reported accident involved a six-year-old girl and a relative who were struck by a truck. The circumstances of the collision and the precise location should be confirmed through police records before further details are published. The incident has renewed attention to the dangers of holding celebrations close to traffic and the need for safe locations where groups can gather without obstructing roads. What the restrictions mean The reported restrictions concern midnight celebrations and cake-cutting activities in the Hussain Sagar area. The exact boundaries, operating hours, legal provisions and penalties should be checked against the relevant police order. Residents should follow instructions issued by traffic police and local authorities. People organising celebrations should choose safe locations away from moving vehicles and avoid blocking footpaths, junctions or emergency access routes. Public safety and enforcement Police restrictions in public spaces are generally intended to reduce hazards and keep traffic moving safely. Their effectiveness depends on clear communication, consistent enforcement and public cooperation. Authorities should publish the complete order so that residents understand where restrictions apply and what activities are prohibited. Clear signage and information from local police stations can help prevent accidental violations. The reported action highlights a wider road-safety concern: even brief gatherings can become dangerous when held too close to moving traffic. Source: The Indian Express — Hyderabad report

Telangana Congress Leaders Join AICC Protest in Delhi

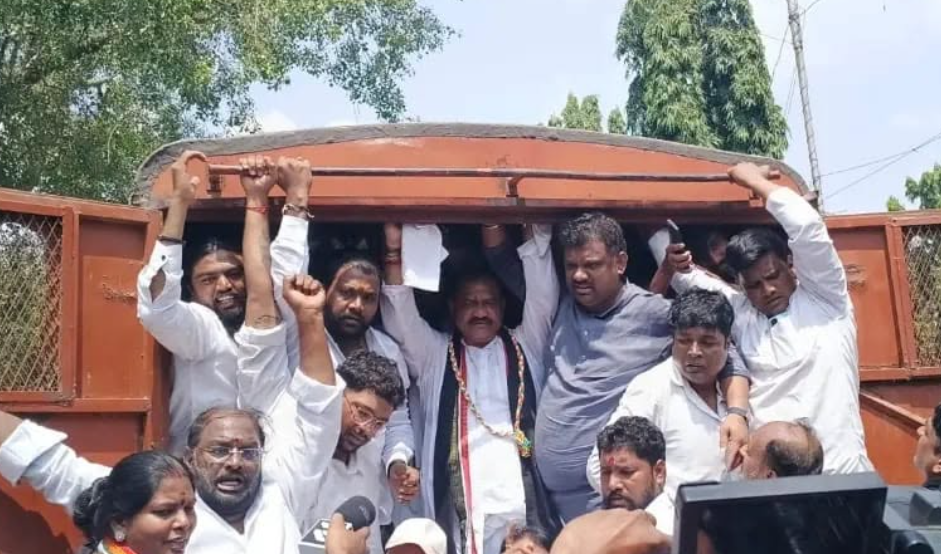
Telangana Congress president B. Mahesh Kumar Goud and other leaders reportedly travel to Delhi for an AICC protest programme. By News National Editorial Team HYDERABAD, October 12, 2026: Several Telangana Congress leaders reportedly travelled to New Delhi to participate in a protest programme organised by the All India Congress Committee (AICC), according to a report published by The Times of India. The reported delegation included Telangana Pradesh Congress Committee president B. Mahesh Kumar Goud and other party representatives. The visit reflects the state unit’s participation in a wider national political campaign. State leaders join national political activity Political parties frequently coordinate programmes between their state organisations and national leadership. Such events provide a platform for leaders to present party positions, mobilise supporters and raise issues they want the public and government to address. The presence of Telangana leaders in Delhi may also help coordinate the state unit’s political messaging with the party’s national strategy. However, the specific demands, participation numbers and outcome of the reported protest should be established through official party statements and independent reporting. Political context Congress leaders have used public demonstrations and organised campaigns to challenge government decisions and raise concerns about governance. The significance of an individual protest depends on its stated demands, the response from authorities and any subsequent political or legal developments. For readers in Telangana, the participation of state leaders is relevant because national political campaigns can influence party organisation, public messaging and future political activity within the state. What to watch next Further developments may include statements from the Congress leadership, reactions from political opponents and details of any memorandum or formal demands submitted during the programme. The protest should be reported as a political event, with the party’s claims clearly attributed. Any disputed allegations should be independently checked before being presented as established facts. Source: The Times of India — Hyderabad report

North Korea Launches Suspected Ballistic Missiles, Japan Says

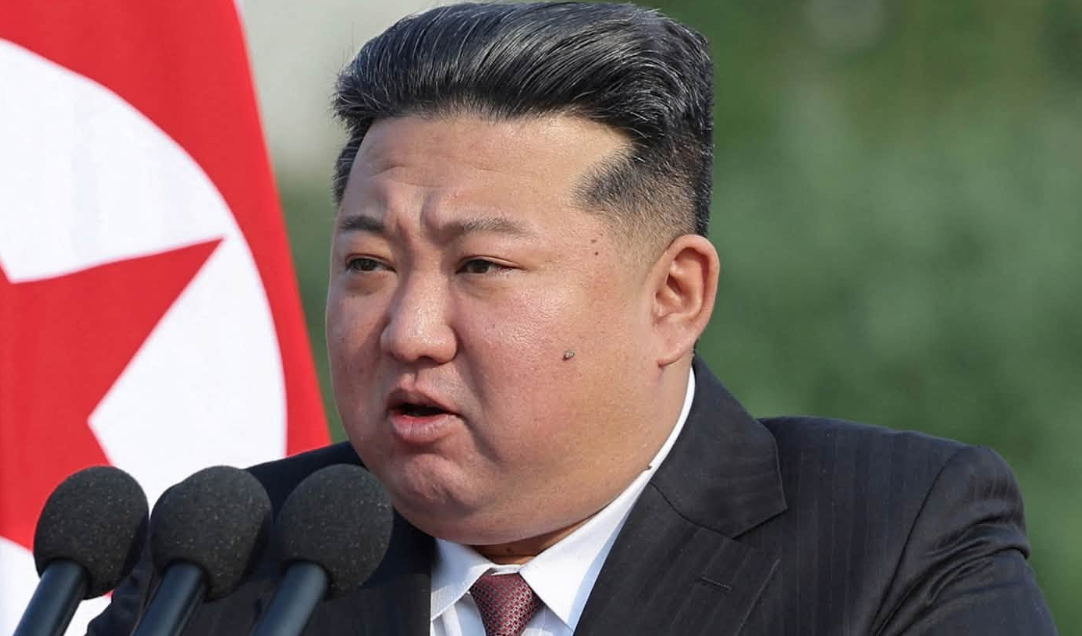
Japan says North Korea launched at least two suspected ballistic missiles on October 12, with authorities assessing their flight paths and regional risks. By News National Editorial Team TOKYO, October 12, 2026: Japan reported that North Korea launched at least two suspected ballistic missiles on Monday, prompting Japanese authorities to gather information and assess possible security implications. Japan's Ministry of Defense said the missiles were launched from inland North Korea during the morning. Initial assessments indicated that they travelled towards the northeast and east before falling near North Korea's eastern coast and into the Sea of Japan. Japanese authorities said the available information did not indicate that the missiles had entered Japanese territory or its exclusive economic zone (EEZ). Japan provides initial flight assessments According to the Japanese Ministry of Defense, the first missile was launched at approximately 9:19 a.m. local time and travelled about 220 kilometres, reaching an estimated maximum altitude of around 20 kilometres. A second launch was detected at approximately 9:36 a.m. That missile reportedly travelled more than 910 kilometres and reached an estimated maximum altitude of around 70 kilometres. These figures are preliminary government assessments. Japanese authorities said the details, including the possibility that one missile followed an unusual trajectory, were being analysed in coordination with the United States and South Korea. The ministry also said it had no confirmed reports of damage at the time of its announcement. Japan orders monitoring and safety measures Japan's government instructed officials to gather and analyse information rapidly, provide timely updates to the public and ensure the safety of aircraft and vessels. Authorities also maintained readiness for any further developments. The launches come amid continued tensions on the Korean Peninsula. North Korea's missile activities have repeatedly prompted security concerns in Japan and South Korea because of the potential risks to regional stability and maritime and aviation safety. The exact technical characteristics and intended purpose of the latest launches had not been fully established in the initial announcement. Regional security implications Japan, South Korea and the United States regularly coordinate their monitoring of North Korean missile activity. Information-sharing helps the governments assess flight paths, potential threats and the technical capabilities involved. Japan described the launches as a serious concern for national and regional security and said it had lodged a strong protest against North Korea. The developments do not, by themselves, establish that a wider military escalation is imminent. Further official assessments will be needed to determine the missiles' characteristics and whether additional security measures are required. Sources: Japan Ministry of Defense, October 12, 2026: https://www.mod.go.jp/j/press/news/2026/10/12e.html Prime Minister's Office of Japan, October 12, 2026: https://japan.kantei.go.jp/105/statement/202610/1012shiji.html ABC News report: https://abcnews.com/International/north-korea-test-fires-suspected-ballistic-missiles-japan/story?id=137186062

AP EDCET 2026 Counselling Registration Deadline October 12

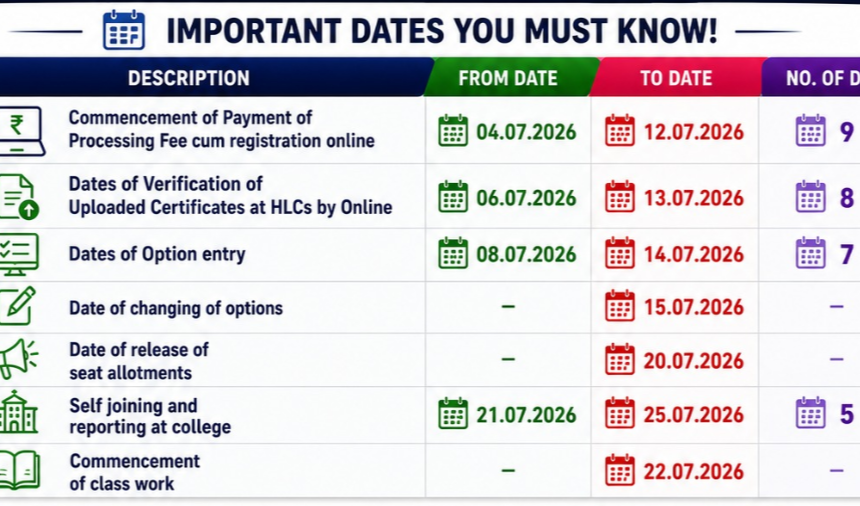
AP EDCET 2026 first-phase counselling registration is listed to close October 12. Check certificate verification and web-option dates. By News National Editorial Team ANDHRA PRADESH, October 12, 2026: Candidates seeking admission to Bachelor of Education (B.Ed.) programmes through the Andhra Pradesh Education Common Entrance Test (AP EDCET) 2026 should check the first-phase counselling schedule carefully, as October 12 is listed as the registration deadline in published counselling information. The counselling process includes registration, document submission and verification, web-option entry and seat allotment. Candidates should follow the official instructions and confirm that each required step has been completed successfully. Important counselling dates According to the published AP EDCET counselling schedule, the main first-phase dates are: October 12, 2026: Listed deadline for first-phase counselling registration. October 6–19, 2026: Published period for online certificate verification. October 13, 2026: Scheduled special-category certificate verification. October 14–18, 2026: Scheduled web-option entry period. October 19, 2026: Scheduled date for changing web options. October 23, 2026: Scheduled first-phase seat allotment. These dates are based on published counselling information and should be reconfirmed through the official portal in case of revisions. What candidates should do Candidates who have not completed registration should immediately check the counselling portal for the current status and any available instructions. They should retain payment receipts, registration details and acknowledgement records. Applicants should also ensure that the required certificates are uploaded correctly and that verification is completed according to the applicable procedure. Registration alone does not necessarily mean that a candidate has completed every stage of counselling. Before entering web options, candidates should review the available colleges, course preferences, eligibility requirements and other admission conditions. They should arrange their preferences carefully and check the portal's instructions before submitting them. Why the web-option stage matters Web-option entry allows eligible candidates to indicate their preferred colleges and courses for seat allocation. Candidates should understand the order of their preferences and the applicable rules before final submission. Seat allotment depends on factors such as merit, eligibility, category, reservation rules, available seats and the preferences submitted by candidates. Completing counselling steps does not guarantee admission to a particular college. Candidates should avoid relying exclusively on social media posts or unofficial messages about deadlines. If an announcement conflicts with the portal, they should seek clarification from the competent counselling authority. Where to verify the schedule Applicants should use the official AP EDCET counselling website or the relevant Andhra Pradesh State Council of Higher Education admissions portal to check notices, registration status and subsequent instructions. Because deadlines can affect admission opportunities, candidates should verify the latest notification before taking action. Sources: Sakshi Education, AP EDCET counselling schedule: https://education.sakshi.com/en/ap-edcet/counselling/ap-edcet-2026-counselling-dates-announced-check-bed-bed-special-admission-schedule-200658 Careers360, AP EDCET counselling dates: https://university.careers360.com/articles/ap-edcet-counselling Official AP EDCET portal: https://cets.apsche.ap.gov.in/EDCET/

AP Local Body Polls Naidu Targets 40% Tickets for BCs

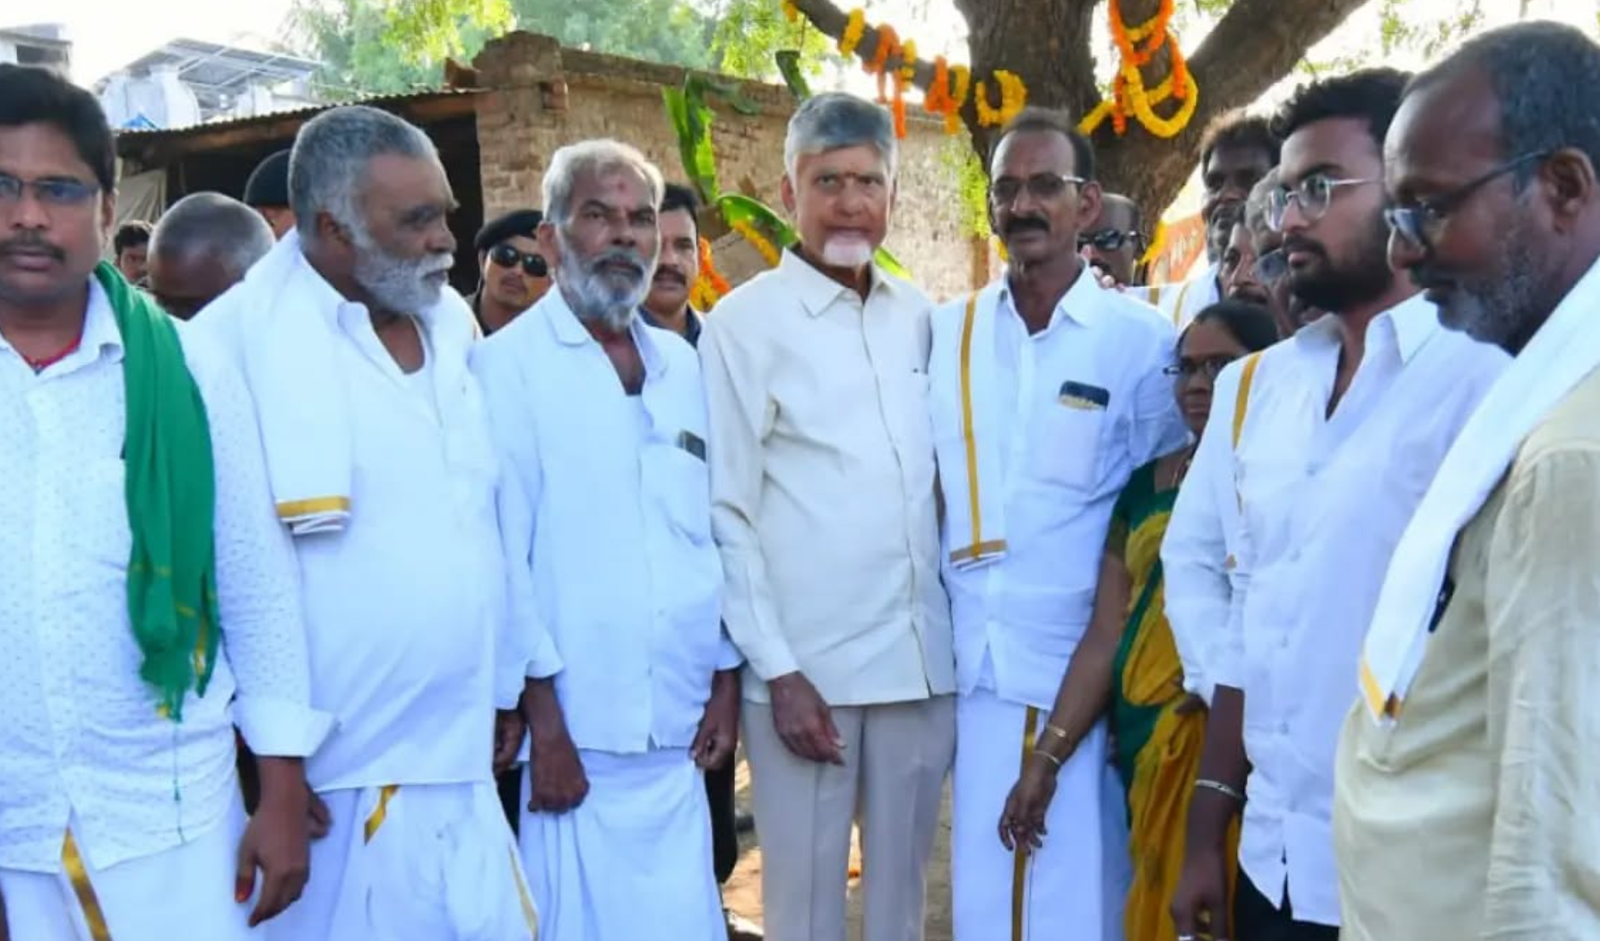
Chandrababu Naidu says the Andhra Pradesh ruling alliance will strive to give up to 40% of local election tickets to BC candidates. Andhra Pradesh Alliance Targets 40% Tickets for BC Candidates in Local Body Elections By News National Editorial Team VIJAYAWADA, October 12, 2026: Andhra Pradesh Chief Minister and Telugu Desam Party (TDP) president N. Chandrababu Naidu has said the ruling alliance will strive to allocate up to 40% of its tickets to candidates from Backward Classes (BCs) in the upcoming local body elections. The announcement puts social representation and candidate selection at the centre of the alliance's preparations for grassroots elections. According to reports published on October 12, Naidu discussed the proposal while addressing party leaders and outlining expectations for the electoral campaign. BC representation becomes a major election issue Naidu said the alliance government had accepted recommendations from the Rajiv Ranjan Mishra Commission concerning BC representation in local bodies. The commission reportedly proposed an average reservation of 28.18% for BCs. The chief minister's stated goal of offering up to 40% of party tickets is a political commitment concerning candidate selection. It should not be confused with a statutory reservation percentage: the two are different measures, and the actual allocation will depend on the applicable election rules and the alliance's final candidate lists. Naidu also criticised the previous YSR Congress Party government over changes to BC reservation levels. Those claims represent the ruling party's political position and should be assessed against the relevant legislation, government orders and court decisions. Candidate selection and alliance coordination Naidu has reportedly instructed ministers, legislators and party functionaries to treat the local body elections as an important test of their organisational performance. Candidate selection is expected to consider electoral prospects, integrity, efficiency and social representation. The alliance includes the TDP, Jana Sena Party and Bharatiya Janata Party. Coordination among the partners will be important when deciding which party contests individual seats and which candidates receive tickets. The parties must also manage expectations among local leaders and grassroots workers, particularly where multiple alliance partners have support in the same constituency. What the announcement means Local body elections influence governance at the village, mandal and municipal levels. These institutions have responsibilities connected with local infrastructure, civic services and community development, making representation an important political issue. If the alliance follows through on its stated target, the final candidate lists will provide a clearer picture of how many BC candidates receive tickets. The impact on elected representation, however, will depend on the results of the elections, not just the number of nominations. The election schedule, reservation rules and final candidate allocations should be checked against official notifications as they become available. Until then, the 40% figure should be reported as the alliance's stated target rather than a completed allocation. Sources: The New Indian Express, October 12, 2026: https://www.newindianexpress.com/states/andhra-pradesh/2026/Oct/12/local-body-elections-an-acid-test-for-coalition-govt-cm-chandrababu-naidu The Times of India, October 12, 2026: https://timesofindia.indiatimes.com/city/vijayawada/andhra-pradesh-local-body-election-tdp-allies-will-strive-to-allot-40-tickets-to-bcs-says-chief-minister-chandrababu-naidu/articleshow/134876646.cms

ASOS Confirms Customer Data Breach After Employee Account Compromise

ASOS says a cyberattack exposed some customer names and contact details after an attacker obtained employee credentials through impersonation. By News National Editorial Team LONDON, October 12, 2026: British online fashion retailer ASOS has confirmed a cybersecurity incident in which an unauthorised person accessed some customers' personal information after obtaining login credentials for an employee account through impersonation. In a customer communication reported by Reuters on October 8, ASOS said its initial investigation found that names, contact details and certain non-personal account-related information had been accessed. The retailer said payment-card information and account passwords were not exposed, according to its findings at that stage.  How the incident happened ASOS said an unauthorised person impersonated a trusted contact to obtain an employee's login credentials. The credentials were then used to access information on certain third-party platforms used by the company. The method is known as social engineering. Instead of relying exclusively on a technical vulnerability, an attacker manipulates a person into disclosing information or taking an action that compromises security. Once an employee account is compromised, the level of access available to that account can determine how much information an attacker can reach. Connections to external services may increase the risk if permissions are broader than necessary or if access is not monitored effectively. ASOS said it immediately locked down the affected platforms. The company also said its website and app remained safe to use throughout the incident and continued to be safe to use after the breach was discovered. It was cooperating with law-enforcement and regulatory authorities, Reuters reported. What information was exposed? The retailer's initial investigation identified customer names, contact details and certain non-personal account-related information as exposed. ASOS said payment-card information and account passwords were not compromised. That distinction is important. There is no basis in the reported company statement to claim that payment-card details or passwords were stolen in this incident. However, contact details can still be valuable to criminals. Information about a customer's relationship with a retailer may help attackers create convincing phishing emails, text messages or phone calls that imitate customer support or delivery services. Customers should be cautious of unexpected messages asking them to click a link, disclose a verification code, confirm account details or make an additional payment. If a message appears suspicious, customers should visit the retailer's official website or app directly rather than using links supplied in the message. The company had not publicly established in the reporting available for this article that the exposed information had been used for further fraud. Any claims about subsequent misuse or the precise number of affected customers should be based on later company or regulator updates. Why employee-account security matters Employee accounts can provide access to customer-service systems, marketing platforms, analytics tools and other third-party services. If an attacker gains control of an account, the resulting exposure may extend beyond the employee's primary workplace computer. Businesses should use strong authentication, including phishing-resistant multi-factor authentication where possible. Employees should be trained to verify unusual requests through a separate communication channel, especially when a message asks for credentials or access to sensitive systems. Companies should also limit employee permissions, monitor unusual login behaviour and review third-party integrations regularly. Access to external platforms should be revoked promptly when credentials may have been compromised. Protecting customers and responding to breaches Retailers should have a clear process for investigating suspected incidents, securing affected accounts, preserving evidence and notifying customers or regulators where required. They should also review the scope of any exposure and communicate confirmed findings without overstating what is known. For customers, the most practical response is to remain alert to suspicious messages and never share one-time passwords or account credentials with someone who contacts them unexpectedly. Customers should use official channels to check whether a request is genuine. A wider warning for online retailers The ASOS incident demonstrates that a company can face a data-security problem through an employee account and a connected external service, even when its public-facing shopping platform remains available. Protecting customer information therefore requires more than securing a website. Employee authentication, third-party permissions, monitoring and incident-response procedures all play a role. The retailer's initial findings offer a clear lesson for online businesses: impersonation can lead to credential theft, and compromised credentials can expose customer information. Strong identity controls and carefully managed access to external platforms can help reduce the risk of similar incidents. Source: Reuters, October 8, 2026: https://www.reuters.com/business/retail-consumer/uks-asos-says-breach-exposed-some-customer-personal-data-2026-10-08/

FBI Data Breach Exposes Sensitive Employee Records After Patch Failure

The FBI confirmed a third-party security failure exposed sensitive employee data, highlighting the importance of timely security patches. By News National Editorial Team WASHINGTON, October 12, 2026: The US Federal Bureau of Investigation (FBI) has removed a contractor following a data breach that exposed sensitive personal information belonging to thousands of bureau employees, according to Reuters reporting published on October 6. The FBI confirmed that a third-party platform suffered a security failure after a contractor failed to implement a security patch. FBI cyber chief Brett Leatherman said the bureau had taken steps to mitigate further risk and protect its workforce. Reuters, citing sources familiar with the matter, identified the platform as Oracle PeopleSoft and the third-party organisation as Accenture. The FBI's public statement did not identify either organisation, and Reuters said it could not independently determine the specific contractor's identity or employment status.  What information was exposed? Reuters reported that the breach affected thousands of FBI employees and exposed sensitive information, including detailed job descriptions, street addresses and medical records. Some records reportedly contained descriptions of counterintelligence roles and addresses associated with human intelligence personnel. The exposure of such information creates risks beyond ordinary privacy concerns. Criminals could potentially use personal and employment details to construct targeted phishing messages, impersonate officials or attempt to obtain further access to restricted systems. The full consequences of the breach were still being assessed in the reporting available for this article. The number of records exposed should not be treated as a precise count of affected individuals unless confirmed by investigators. The importance of applying security patches Reuters reported that the hacking group ShinyHunters claimed to have exploited a weakness in PeopleSoft to access the FBI's job site. In June, Google had raised concerns about a ShinyHunters-linked hack-and-extort campaign involving organisations using PeopleSoft, while Oracle issued a security alert and fixes. The FBI's explanation specifically identified a failure to apply a security patch. However, Reuters said it could not determine when or whether the relevant system administrators had followed earlier patching recommendations. Enterprise applications can be difficult to update because they support essential business processes and require testing. But delaying a critical patch without effective compensating controls can leave a known weakness available to attackers. Third-party risk and accountability Public agencies and private companies often rely on contractors to operate software, maintain systems and manage employee information. These relationships can provide technical expertise, but they also create dependencies that must be monitored. Contracts should clearly define responsibility for reviewing security alerts, applying updates, testing fixes and reporting incidents. Organisations should verify that these tasks have been completed rather than relying solely on assurances from suppliers. Accenture told Reuters that it remained proud to support the FBI's mission. The company did not answer Reuters' questions about the contractor or the alleged failure to apply the patch. The reported removal of a contractor is an employment action, not a court finding of criminal liability. The technical cause identified by the FBI should be distinguished from details that Reuters attributed to unnamed sources. Lessons for organisations Organisations holding sensitive employee data should maintain an inventory of applications and the teams responsible for them. Critical patches should be prioritised, tested and verified, with exceptions documented and reviewed. Access to human-resources databases should be restricted to authorised personnel. Companies should monitor unusual data access, preserve logs and establish procedures for investigating suspected breaches. Third-party providers should be included in incident-response exercises and security reviews. The FBI incident illustrates how a weakness in a supporting platform can expose sensitive information even at an organisation with substantial security resources. Effective patch management and clear accountability across supplier relationships remain essential to reducing that risk. Sources: Reuters, October 6, 2026: https://www.reuters.com/technology/accenture-contractor-removed-fbi-following-damaging-data-breach-sources-say-2026-10-06/ Oracle security updates: https://www.oracle.com/security-alerts/

South Korea and Japan Investigate Cyberattacks Amid AI Security Concerns

South Korean banks and Japanese companies are investigating cyberattacks as authorities examine whether AI tools helped attackers. By News National Editorial Team SEOUL/TOKYO, October 12, 2026: Banks and businesses in South Korea and Japan are strengthening cybersecurity measures following a wave of reported attacks that has raised concerns about how artificial intelligence may be helping cybercriminals. Investigations are continuing, and authorities have not established that AI was used in every incident. Reuters reported on October 9 that nine South Korean banks and two large churches were investigating cyberattacks. Japanese companies, including Daiwa Securities, SoftBank and Lawson, were also among organisations affected by a recent increase in cyber incidents. South Korean financial institutions investigate breaches South Korean President Lee Jae Myung said earlier in October that recent attacks on banks appeared to involve AI tools. Reporting by the Financial Times said data at seven financial firms had been compromised, including customer information at several banks and savings institutions. Authorities were investigating the incidents and the methods used to access the affected systems. Cybersecurity researchers and investigators have examined whether AI-assisted tools were used to identify software weaknesses or accelerate other parts of the attacks. Reuters reported that a cybersecurity firm assessed that AI assistance probably played a role in incidents linked to a suspected China-based attacker. That is a reported assessment, not a final judicial finding. The exact method, extent of access and potential impact differ by incident. It would be inaccurate to describe every reported attack as an AI-driven breach or to assume that all affected organisations suffered the same type of data loss. How AI may change cybercrime Artificial intelligence can help automate certain technical and administrative tasks. In a criminal context, that may include analysing public information, generating convincing phishing messages, assisting with code or helping identify potential weaknesses in exposed systems. These capabilities can reduce the time required for some activities, but AI does not automatically make an attack successful. Many intrusions still depend on familiar weaknesses such as unpatched software, stolen credentials, excessive permissions or inadequate monitoring. For defenders, the challenge is to detect suspicious behaviour while distinguishing malicious automation from legitimate system activity. AI-based security products may help analyse large volumes of events, but they also require careful configuration and human oversight. Japan faces a wider rise in cyber incidents Reuters reported that Japanese companies including Daiwa Securities, SoftBank and Lawson had faced recent cyber incidents. The report described an environment in which businesses were racing to improve their defences as attacks became more frequent. Separately, data cited in Reuters reporting indicated rising cyber incidents in South Korea. Figures from national reporting systems and private cybersecurity companies use different methods and definitions, so they should not be compared as if they measured precisely the same thing. Nevertheless, the incidents have prompted concern among businesses that rely on digital services and handle large volumes of customer or financial information. Regulators and companies respond South Korea's financial authorities have called on institutions to review their security posture and improve their ability to detect and respond to attacks. Organisations can reduce exposure by enforcing multi-factor authentication, promptly applying security updates, limiting access to sensitive systems and monitoring unusual account activity. Banks and technology companies should also test their incident-response plans, preserve logs and examine third-party connections. Employee training remains important because phishing and impersonation can provide attackers with access even when technical controls are in place. What the developments mean internationally The incidents in East Asia are relevant to organisations around the world, including Indian banks, fintech companies and online businesses. Attackers do not need advanced AI tools to exploit weak controls, but automation may make some techniques easier to repeat at scale. The immediate priority is to establish what happened in each case, notify affected customers where required and address the weaknesses identified by investigators. As authorities release more findings, the precise role of AI and the scope of individual breaches may become clearer. Sources: Reuters, October 9, 2026: https://www.reuters.com/legal/litigation/south-korea-japan-buffeted-by-hacks-ai-lowers-bar-cybercriminals-2026-10-09/ Financial Times, reporting on South Korean financial-sector cyberattacks: https://www.ft.com/content/fb32e9f8-4bf7-44ad-983d-1a03f50f66f5

CERT-In Warns of MikroTik RouterOS SSH Vulnerability

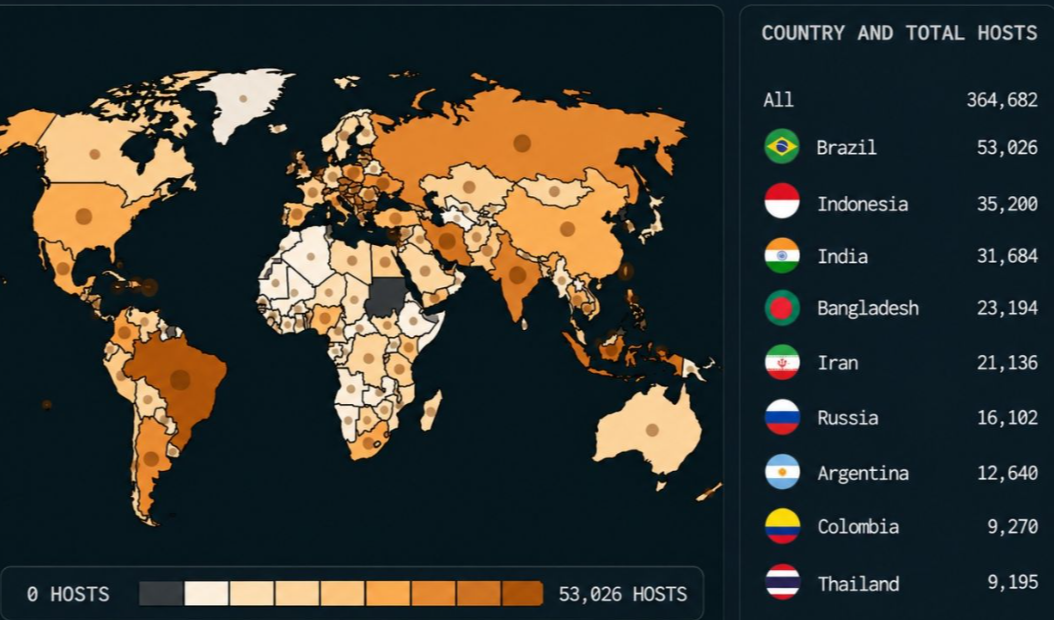
CERT-In warns of a MikroTik RouterOS SSH flaw. The vendor says CVE-2026-67279 has been exploited in the wild and lists fixed versions By News National Editorial Team NEW DELHI, October 12, 2026: India's cybersecurity agency has warned network administrators about a vulnerability in MikroTik RouterOS that could allow an unauthenticated remote attacker to bypass the expected Secure Shell (SSH) login process and perform unauthorised operations on affected devices. CERT-In published Vulnerability Note CIVN-2026-0494 on October 9, identifying the flaw as CVE-2026-67279. The agency said exploitation could allow unauthorised operations involving files managed by RouterOS, including files containing configuration and diagnostic information. MikroTik's own security notice says this SSH vulnerability has been exploited in the wild. What the flaw allows SSH is commonly used by administrators to manage routers and other network devices remotely. The vulnerability involves the handling of authentication and rekeying in the SSH implementation of affected RouterOS versions. CERT-In said an attacker who can reach the SSH service could potentially open a session channel and send an execution request without completing the expected authentication workflow. The resulting access could permit file creation, modification or reconstruction within the RouterOS-managed file namespace. The warning does not mean every MikroTik router is vulnerable. Exposure depends on the installed software version and whether the affected management service is reachable by an attacker. Which versions are affected? CERT-In lists the following affected ranges: RouterOS 6.0.0 to versions earlier than 6.49.21. RouterOS 7.0.0 to versions earlier than 7.23.4. RouterOS 7.24 to versions earlier than 7.24.2. MikroTik identifies fixed versions for this vulnerability as 6.49.21, 7.23.4 and 7.24.2, or later releases containing the relevant fix. Administrators should consult the vendor's current security guidance before updating, particularly because the vendor has also documented other RouterOS vulnerabilities with separate patch requirements. Why network administrators should act Routers often sit at the boundary between internal systems and the public internet. They may connect offices, servers, remote workers and cloud services. A compromised device could therefore expose configuration details or provide an attacker with a foothold for further activity. Small businesses, educational institutions, internet service providers and enterprises should identify all RouterOS devices in their networks. Devices that have not been updated may remain vulnerable even if they appear to be operating normally. CERT-In's notice establishes that the vulnerability exists. MikroTik's statement about exploitation in the wild adds urgency, but it does not establish that a particular Indian organisation has been attacked through this flaw. Recommended security steps Administrators should check the installed RouterOS version and apply the appropriate vendor security update. They should restrict SSH access to trusted management networks and disable remote administration where it is not required. Organisations should also review logs for unexpected login attempts, new files, unexplained configuration changes and suspicious outbound traffic. Strong unique credentials, multi-factor authentication where supported, network segmentation and tested backups provide additional protection. If compromise is suspected, teams should preserve logs and configuration snapshots, rotate potentially exposed credentials and follow their incident-response procedures. A wider lesson for infrastructure security Network devices are sometimes overlooked in patching programmes because they are viewed as stable infrastructure rather than active computing systems. The MikroTik advisory shows why routers require the same disciplined inventory, monitoring and update processes applied to servers and endpoints. Organisations should use official advisories to prioritise remediation and verify that patches have actually been installed. For affected MikroTik users, checking the version and applying the vendor's fix are immediate practical steps. Sources: CERT-In, Vulnerability Note CIVN-2026-0494, October 9, 2026: https://www.cert-in.org.in/s2cMainServlet?VLCODE=CIVN-2026-0494&pageid=PUBVLNOTES01 MikroTik security advisories: https://mikrotik.com/supportsec

CERT-In Warns of Cyberattacks Targeting India's Payment APIs

CERT-In warns Indian fintech and lending firms of cyberattacks exploiting payment APIs and stolen credentials to enable unauthorised transfers. By News National Editorial Team NEW DELHI, October 12, 2026: India's national cybersecurity agency has issued a critical warning about cyberattack campaigns targeting non-banking financial companies, digital lending platforms, fintech businesses, payment service providers and digital wallet operators. The attacks exploit weaknesses in internet-facing applications and payment application programming interfaces (APIs), potentially allowing criminals to initiate unauthorised fund transfers. The Indian Computer Emergency Response Team (CERT-In) published Advisory CIAD-2026-0046 on October 9. It describes campaigns in which attackers compromise exposed applications, steal payment gateway or partner-bank API credentials and use those credentials to call disbursement or transfer functions directly. How attackers exploit payment systems According to CERT-In, some attacks exploit deprecated or unauthenticated APIs, unrestricted file-upload functions, outdated middleware and credentials stored in source code or configuration files. Other identified weaknesses include long-lived static API tokens and remote services without multi-factor authentication. After gaining access, attackers may obtain credentials used by payment aggregators, banks or lending partners. They can then attempt to initiate transfers from within infrastructure that the financial institution already trusts. The agency said fraudulent transactions observed in these campaigns included dummy reference identifiers and transfers to attacker-controlled mule accounts. It also reported cases involving multiple high-value transactions and attempts to remove logs or tamper with endpoint security tools. CERT-In noted possible use of AI-assisted offensive tools. That observation should not be interpreted as confirmation that artificial intelligence was used in every attack. Why the issue matters for Indian fintech Digital lenders and payment companies depend on connected systems to approve transactions, verify customers, check beneficiaries and process disbursements. If a transfer API accepts a valid credential without independently verifying the transaction's approval status, an attacker may exploit the gap between the application and the payment system. A successful compromise could result in financial losses, customer disputes, regulatory scrutiny and service disruption. However, the advisory does not establish that every organisation in the affected sectors has been breached, nor does it provide a single nationwide loss figure for the campaigns. Security measures recommended CERT-In recommends multi-factor authentication for payment platforms, administrative portals, APIs and remote access. It also advises organisations to maintain a complete inventory of active APIs and formally disable services that are no longer required. Financial institutions should ensure that every payout is checked against an approved transaction record. Payment-stage controls should enforce transaction limits and beneficiary verification rather than relying solely on checks performed earlier in an application workflow. Other measures include secure management and rotation of API credentials, restricted outbound connections from production systems, centralised log retention, endpoint detection with tamper protection and regular API security testing. Companies should also reconcile payment records with bank and aggregator statements to identify discrepancies quickly. If suspicious transfers or compromised credentials are detected, the agency advises organisations to disable affected accounts, suspend vulnerable APIs where necessary, preserve forensic evidence and report relevant incidents to CERT-In/CSIRT-Fin. What businesses should do now Fintech firms should review their payment APIs, privileged access and transaction-validation controls without waiting for a confirmed breach. Banks and financial institutions should also assess the security of third-party services connected to their systems. The October 9 advisory is a warning about observed attack campaigns, not proof that all Indian payment systems are compromised. Its practical message is that payment security must extend beyond the customer-facing application to the APIs and credentials that actually authorise transfers. Sources: CERT-In, Advisory CIAD-2026-0046, October 9, 2026: https://www.cert-in.org.in/s2cMainServlet?VLCODE=CIAD-2026-0046&pageid=PUBVLNOTES02 CERT-In official website: https://www.cert-in.org.in/